What Is Spear Phishing and Why Targeted Attacks Hit Harder
Last updated: October 14, 2026
Spear phishing is a personalized email attack that uses trusted context to make one recipient approve a payment, reveal credentials, or share sensitive information. In 2025, Canadians reported C$67.9 million in spear-phishing losses to the Canadian Anti-Fraud Centre. That total came from 813 reports and 571 victims. Only investment fraud cost Canadians more.
You may be reviewing an invoice while messages keep arriving, when an email appears to come from a supplier you already use. The tone sounds normal, the project name is correct, and the request fits your role. Nothing looks like the cartoon version of a scam.
That's why spear phishing deserves a different response from ordinary spam. We'll look at how targeted attacks work, why careful people still miss them, and which technical and business controls stop one mistaken click from becoming a payment or account takeover.
What Spear Phishing Means
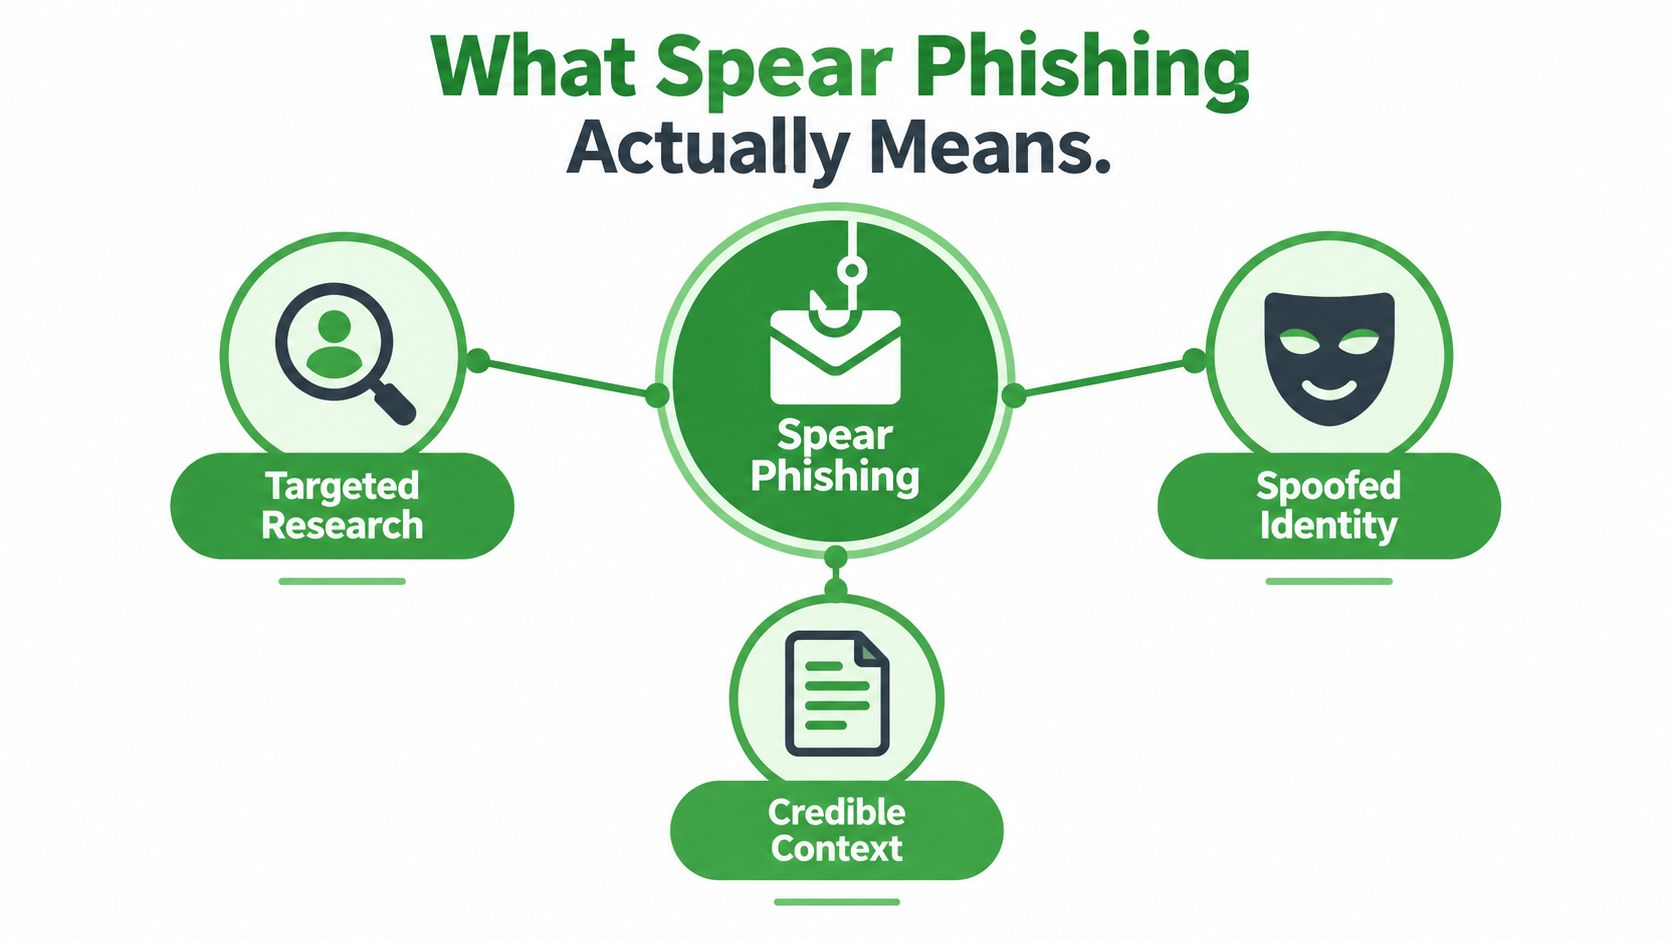
Spear phishing is targeted deception by email or another message channel. An attacker researches a person or small group, impersonates a trusted identity, and shapes a request around the recipient's work or personal context. Relevance is the main hook. A polished design may help, but familiarity makes the request easier to accept.
Consider a small-business example. An accounts payable clerk receives an email that appears to come from a real supplier. It uses the supplier's usual sign-off, mentions a recent order, and asks the clerk to update banking details before the next payment. The attacker might find the employee's role on the company website, learn about the supplier relationship from a public announcement, or gain access to an existing email thread.
The request fits the employee's normal duties and arrives at a plausible time. That combination can defeat a quick review. If the new banking information is accepted without independent confirmation, the next payment may go to the attacker.
The trust substitution principle
A useful mental model is trust substitution. The attacker replaces a genuine identity or request with a false one, then counts on an authorized employee to complete the action.
Spear phishing can succeed without a software exploit. The attacker may never enter the payment system directly. Instead, they persuade someone with legitimate access to approve a payment, change supplier details, disclose a password, or open a document.
The Canadian Centre for Cyber Security's cyber hygiene guidance describes spear phishing as a customized social-engineering tactic that uses details about a person's job, interests, or characteristics. Its checks include confirming that you know the sender, that the tone matches normal communication, and that a link or attachment belongs in the message.
Those checks are useful, but awareness alone has limits. Personalized messages turn a routine request into a recognition test, and a busy recipient may miss the warning. The recipient becomes the vulnerability because the request looks routine. Treat every unexpected payment, password, or account-change request as untrusted until you verify it through a separate channel, such as a known phone number or a new message thread.
Spear Phishing Versus Regular Phishing
A generic phishing email is like a flyer dropped into thousands of mailboxes. The sender repeats a fake delivery notice, account warning, or password-reset message and waits for a few recipients to click.
Spear phishing works more like a forged note addressed to one person. The attacker selects a target, gathers context, and shapes the message around a role, relationship, or current project. “Your account is locked” is generic. A request mentioning your actual manager, supplier, or live contract feels connected to work, which makes the recognition failure harder to spot.
| Dimension | Regular Phishing | Spear Phishing |
|---|---|---|
| Audience | Large, broad recipient groups | One person, team, or organization |
| Personalization | Limited or copied from a generic template | Based on names, roles, relationships, and events |
| Typical goal | Clicks, credentials, malware, or small payments | Payment diversion, account takeover, sensitive data, or privileged access |
| Message style | Often urgent but vague | Urgent and operationally believable |
| Useful warning signs | Strange links, attachments, spelling, and generic greetings | Lookalike domains, unusual requests, reply-to mismatches, timing, and process changes |
| Main defence | Filtering and cautious clicking | Filtering, account protection, independent verification, and dual approval |
The number of messages is not the whole risk. In 2025, reported Canadian spear-phishing losses averaged about C$118,900 per victim, based on CAFC figures. Reported losses are a lower bound because individuals and organizations do not always report fraud.
A targeted payment request may contain no malicious link. An attacker can impersonate an executive or supplier and ask for a transfer using an ordinary reply. That pattern is closely associated with business email compromise. Whaling and executive email fraud is one targeted form, while other attacks imitate suppliers, colleagues, or service providers.
Awareness training helps people notice warning signs, but it cannot reliably confirm identity during a busy workday. Small teams need layers: filtering, account protection, clear payment procedures, dual approval, and independent verification. Confirm a changed bank detail or unusual transfer through a known phone number or a separate message thread, not through contact information in the email.
Practical rule: Generic phishing asks, “Will anyone click?” Spear phishing asks, “Who has the authority to do this, and what would make the request feel normal?”
How a Spear Phishing Attack Unfolds
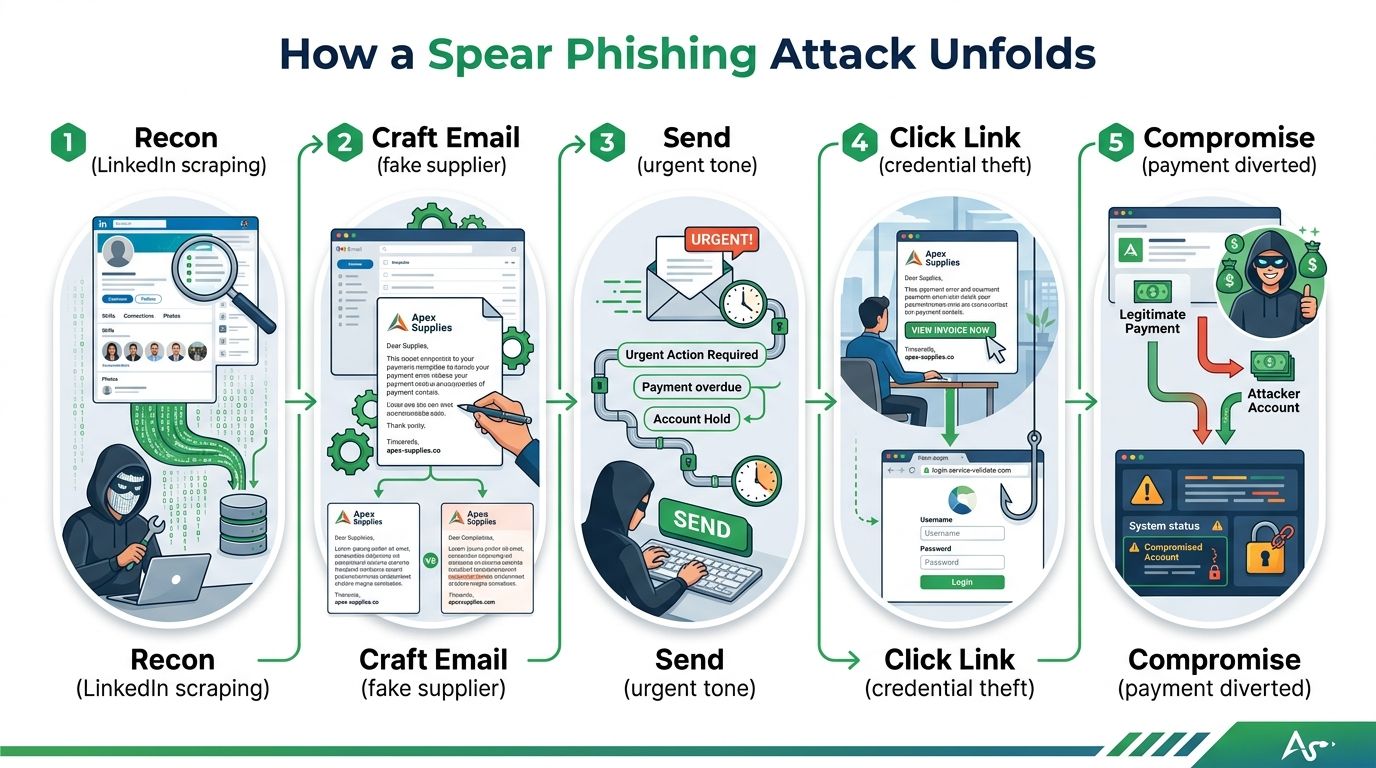
A targeted attack may begin days or weeks before an email appears. The attacker studies people, relationships, systems, and upcoming events, then uses those details to make a request sound routine.
A small design firm announces a new contract. An attacker checks its public staff page, finds the person who handles invoices, and reviews the owner's role and supplier relationships. A LinkedIn profile may reveal the finance employee's title, while the company website supplies the project context needed for a believable message.
Five stages in a typical attack
Reconnaissance: The attacker gathers names, job roles, supplier relationships, and project timing from public pages. They may also use a compromised mailbox or exposed credentials.
Identity selection: The attacker decides whether to imitate a supplier, executive, financial institution, or colleague. They may register a lookalike domain or take control of a genuine account.
Message construction: The email copies the sender's tone and refers to a real business event. A payment-change request might follow a contract announcement. An executive request might arrive during payroll or another transaction period.
Action request: The recipient is asked to approve a transfer, open an attachment, enter credentials, or provide information. The wording usually sounds like ordinary work rather than an emergency.
Follow-on activity: After a click or login, the attacker may watch conversations, create forwarding rules, grant an application access, or send a more convincing message from the account.
A link may open a fake Microsoft or Google sign-in page. In an adversary-in-the-middle attack, that page proxies the connection between you and the service. You can enter the correct password and complete multifactor authentication, yet the attacker may capture the active session token.
Each stage offers a chance to interrupt the chain. Email authentication can reduce direct domain spoofing. Mailbox alerts can reveal unusual logins or forwarding rules. Independent payment checks can stop a fraudulent transfer even if the message passes through every filter. For small teams, those layers matter because awareness training cannot verify identity on a rushed workday.
Why Targeted Attacks Are So Hard to Spot
Many security guides teach people to look for spelling errors, strange links, and unfamiliar attachments. Those checks still matter, but they don't cover the hardest cases.
The federal Get Cyber Safe Awareness Tracking Survey found that 87% of online Canadians recognize requests for sensitive information as a phishing sign. Another 86% recognize unfamiliar links or incorrect sender addresses. Yet the share who said they’d been a victim of a phishing attack rose from 18% in 2022 to 26% in 2026 (Get Cyber Safe Awareness Tracking Survey).
Recognition and prevention aren't the same thing. A well-personalized message can contain the correct names, a familiar writing style, and a real project reference. A trained employee may notice the request feels unusual, but pressure, workload, and authority can still push them to act.
Design for mistakes, not perfect judgement
The answer isn't to blame users or demand that everyone become a forensic email analyst. Build a workflow where one mistaken decision can't independently move money or expose an account.
Useful controls include:
External-sender labels: Mark messages that originate outside your organization, even when the display name matches an executive.
Lookalike-domain detection: Flag domains with extra characters, unusual subdomains, or newly observed infrastructure.
Anomaly alerts: Watch for unusual sender-recipient relationships, unexpected login geography, and unfamiliar attachments or URLs.
Phishing-resistant MFA: Use passkeys or FIDO2 security keys for privileged accounts. These bind authentication to the genuine website more effectively than a code or approval prompt.
Out-of-band verification: Confirm payment, payroll, password-reset, and supplier-account requests using a known phone number or an independently opened account.
The Canadian Centre for Cyber Security's National Cyber Threat Assessment identifies spear phishing as a fraud type with a high reported financial impact. The same guidance supports a layered approach because filtering alone can't detect a request sent from a compromised, legitimate mailbox.
A good security process doesn't require every employee to identify every fake. It makes high-risk actions difficult to approve from email alone.
The modern risk also includes session theft. A password manager and MFA can reduce many credential attacks, but a convincing proxy page may capture an authenticated session unless your organization uses phishing-resistant authentication, conditional access, device checks, and rapid token revocation. Logging should support investigation without collecting more employee content than the business needs, especially when personal information falls under PIPEDA obligations.
Real Spear Phishing Examples
The most useful spear phishing email examples rarely contain glaring mistakes. They show how a request can match current business activity while bypassing normal checks.
The executive wire request
A finance employee receives a brief message that appears to come from the chief executive. The company is handling a confidential acquisition, so a request to pay an adviser quickly sounds plausible. The message asks the employee to keep the transfer private and supplies new recipient-account instructions.
Possible warning signs include secrecy, urgency, a different reply-to address, or a request that skips the usual approval process. A suspicious link or poor grammar may be absent. The message might contain no link at all, which makes the requested action, rather than the writing quality, the main clue.
The supplier banking change
An email that appears to come from a supplier’s genuine contact includes an updated banking form after the company announces a new contract. The timing feels right, and the employee already expects an invoice. The attacker may have spoofed the supplier's domain or compromised someone already involved in the conversation.
The key warning is the change to payment instructions. Confirm it through a known phone number, not the number shown in the email or form. Require a second person to approve the update before sending payment. This small pause works like a second lock on a door, especially when the message itself looks routine.
The shared document login
An email that appears to come from a colleague links to a shared document for a current project. The page resembles a Microsoft or Google sign-in screen and may include the organization's branding. The recipient enters the correct password and completes MFA. As covered earlier, a proxy page can capture the session token even after MFA.
A domain can differ by only a few characters, such as rnicrosoft.com instead of microsoft.com. Polished fakes can make that distinction difficult to notice, so open the service through a saved bookmark or known application, then locate the document inside the account. Our guide to spotting dangerous phishing email examples covers inspection habits that support this workflow.
Across these examples, the attacker's goal is familiar work. Treat unusual secrecy, new payment details, and unexpected sign-in requests as separate verification triggers, even when the sender and timing seem credible.
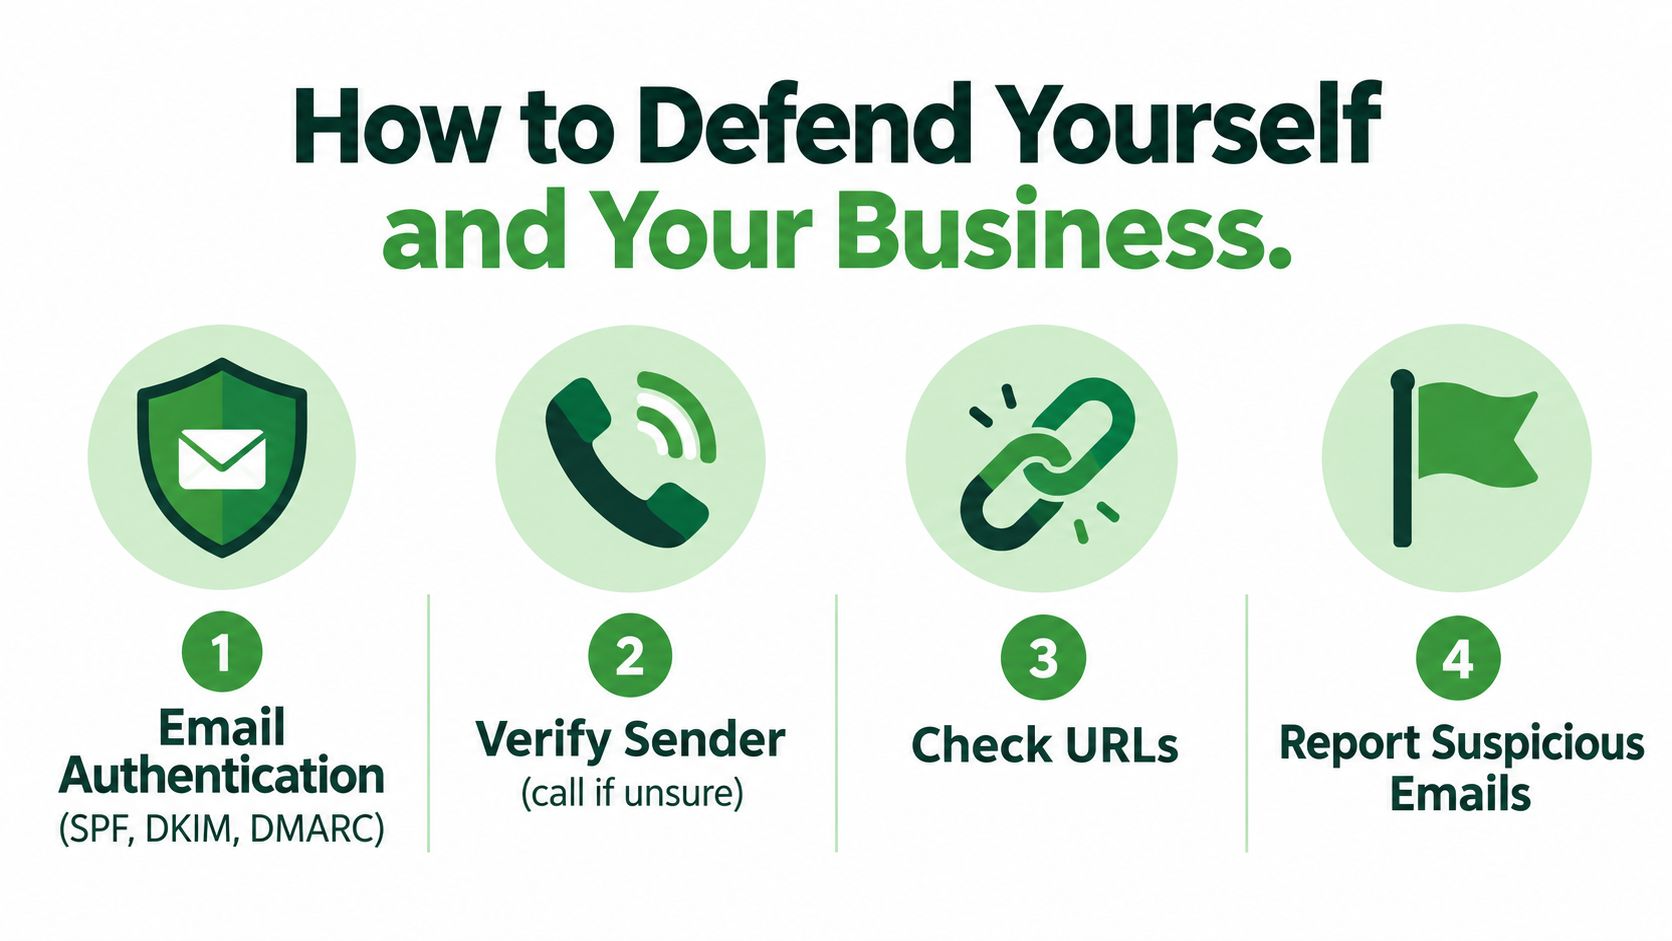
How to Defend Yourself and Your Business
Layered protection works better than a single warning banner or annual training session. We recommend starting with controls that reduce impersonation, then adding account safeguards and business rules that limit the damage.
Start with the email foundation
SPF, or Sender Policy Framework, lets a domain publish which mail servers may send messages for it. DKIM, or DomainKeys Identified Mail, adds a cryptographic signature that receiving systems can check. DMARC, or Domain-based Message Authentication, Reporting, and Conformance, tells receiving systems how to handle messages that fail alignment checks.
These standards can reduce direct domain spoofing, but they don't prove that a genuine mailbox hasn't been compromised. They also won't stop an attacker from registering a similar domain. Use authentication alongside lookalike-domain detection, external-sender labels, URL inspection, attachment scanning, and alerts for unusual sender behaviour.
Protect accounts and transactions
Use MFA across business systems, with FIDO2 security keys or passkeys for administrators and other privileged users where possible. Push approvals are useful, but they can still be abused through repeated prompts or social engineering. Phishing-resistant methods reduce the chance that a fake login page can reuse the authentication.
Your business process matters just as much:
Payment changes: Confirm them by calling a known number already stored in your records.
High-value transfers: Require two people to approve the request.
Credential resets: Never treat an email alone as proof of identity.
Reporting: Give staff a simple, blame-free way to report suspicious messages.
Mailbox monitoring: Alert on new forwarding rules, OAuth grants, mailbox delegation, and unusual sign-ins.
The Canadian Centre for Cyber Security's social-engineering guidance recommends MFA, incident planning, software patching, spam filtering, malicious-domain blocking, and prompt action after someone clicks or downloads something. If a click happens, report it quickly, change affected passwords, reset MFA, and scan the device.
Where a private email provider fits
Typewire is one option for people who want ad-free email, phishing detection, virus filtering, spy-pixel blocking, and zero-access encryption without behaviour tracking. We host email in Canada on our own infrastructure in Vancouver, support custom domains and aliases, and offer unlimited sending on paid plans. Those features can reduce tracking and exposure, but they don't replace independent payment verification, MFA, or a written incident process.
You can also review an email's technical details with our guide to reading an email header and spotting a fake sender. Headers can reveal mismatched paths and authentication results, although a compromised legitimate account may still pass ordinary checks.
What to do after a spear phishing attempt
If someone clicks, replies, or approves a suspicious request, move quickly. Preserve the message with its full headers, revoke active sessions, rotate affected credentials, and contact the bank if money or banking details were involved.
Check mailbox forwarding rules, OAuth grants, delegated access, and recent sign-ins. Notify your security or IT contact, document what happened, and report suspected fraud to the Canadian Anti-Fraud Centre.
A small-business policy can be short:
Payment instructions, payroll changes, supplier banking updates, and credential resets require independent verification. High-risk transfers require two authorized approvers. Staff must report suspicious messages immediately, without fear of blame.
Frequently asked questions
Does MFA stop spear phishing?
Not completely. Multifactor authentication blocks many attacks that rely on a stolen password. But some fake login pages act as a proxy between you and the real service. When you sign in and approve the MFA prompt, the attacker can capture your active session. Phishing-resistant methods, such as passkeys or FIDO2 security keys, offer stronger protection. Pair them with conditional access, device checks, and the ability to revoke sessions quickly.
Does reporting spear phishing help?
Yes. Reporting a suspicious email quickly gives your team time to warn other staff before they respond. It also lets you block the sender’s domain, revoke compromised sessions, and preserve evidence. If money was sent, a fast call to your bank improves the chance of stopping the transfer. Reports to the Canadian Anti-Fraud Centre also help authorities track fraud trends. The centre estimates only 5 to 10% of victims report.
How can I tell if a polished email is real?
Don’t judge an email by how it looks. Spear phishing messages often use correct names, real project details, and a familiar writing style. Focus on what the email asks you to do instead. If it changes payment details, requests credentials, or skips your normal approval process, verify it separately. Call the sender using a phone number you already have on file, or start a new email thread.
What is the difference between spear phishing and whaling?
Whaling is a type of spear phishing that targets senior executives or the people who act on their behalf. Spear phishing can target anyone, such as an accounts payable clerk or a new hire. Whaling aims higher, because executives can approve large payments or access sensitive data. Both rely on research and personalized messages. The main difference is who the attacker chooses as the target.
How do I report spear phishing in Canada?
If you lost money or shared banking details, contact your financial institution first. Then contact your local police and report the incident online at reportcyberandfraud.canada.ca. You can also call the Canadian Anti-Fraud Centre at 1-888-495-8501. Inside your organization, alert your IT or security contact right away. Keep the original email with its full headers, since investigators may need it.
We provide private, ad-free email with phishing detection, virus filtering, spy-pixel blocking, zero-access encryption, and Canadian-hosted infrastructure. If you want an email setup that reduces tracking while supporting safer communication habits, visit Typewire and start with the seven-day free trial.
The post What Is Spear Phishing and Why Targeted Attacks Hit Harder appeared first on Typewire.
What Is Spear Phishing and Why Targeted Attacks Hit Harder
Posted: 2026-10-16
What Is Smishing and How to Avoid SMS Phishing
Posted: 2026-10-13
How to Whitelist an Email Address (So You Stop Missing Messages)
Posted: 2026-10-06
Email Bounce Explained: Soft vs Hard Bounces & How to Fix Them
Posted: 2026-10-02
Which Secure Email Provider Fits Your Workflow? 10 Options by Use Case
Posted: 2026-09-29
Personal Data Privacy: Why Your Email Is the Master Key to Your Digital Life
Posted: 2026-09-24
Secure Email Gateway Guide: Do You Need One?
Posted: 2026-09-23
Average Email Deliverability Rate: 2026 Benchmarks
Posted: 2026-09-18
Phishing vs Spam: What’s the Difference?
Posted: 2026-09-15